Spam Filter Triggers That Kill Cold Email Deliverability
Authentication failures now cause permanent rejections that better copy cannot fix.
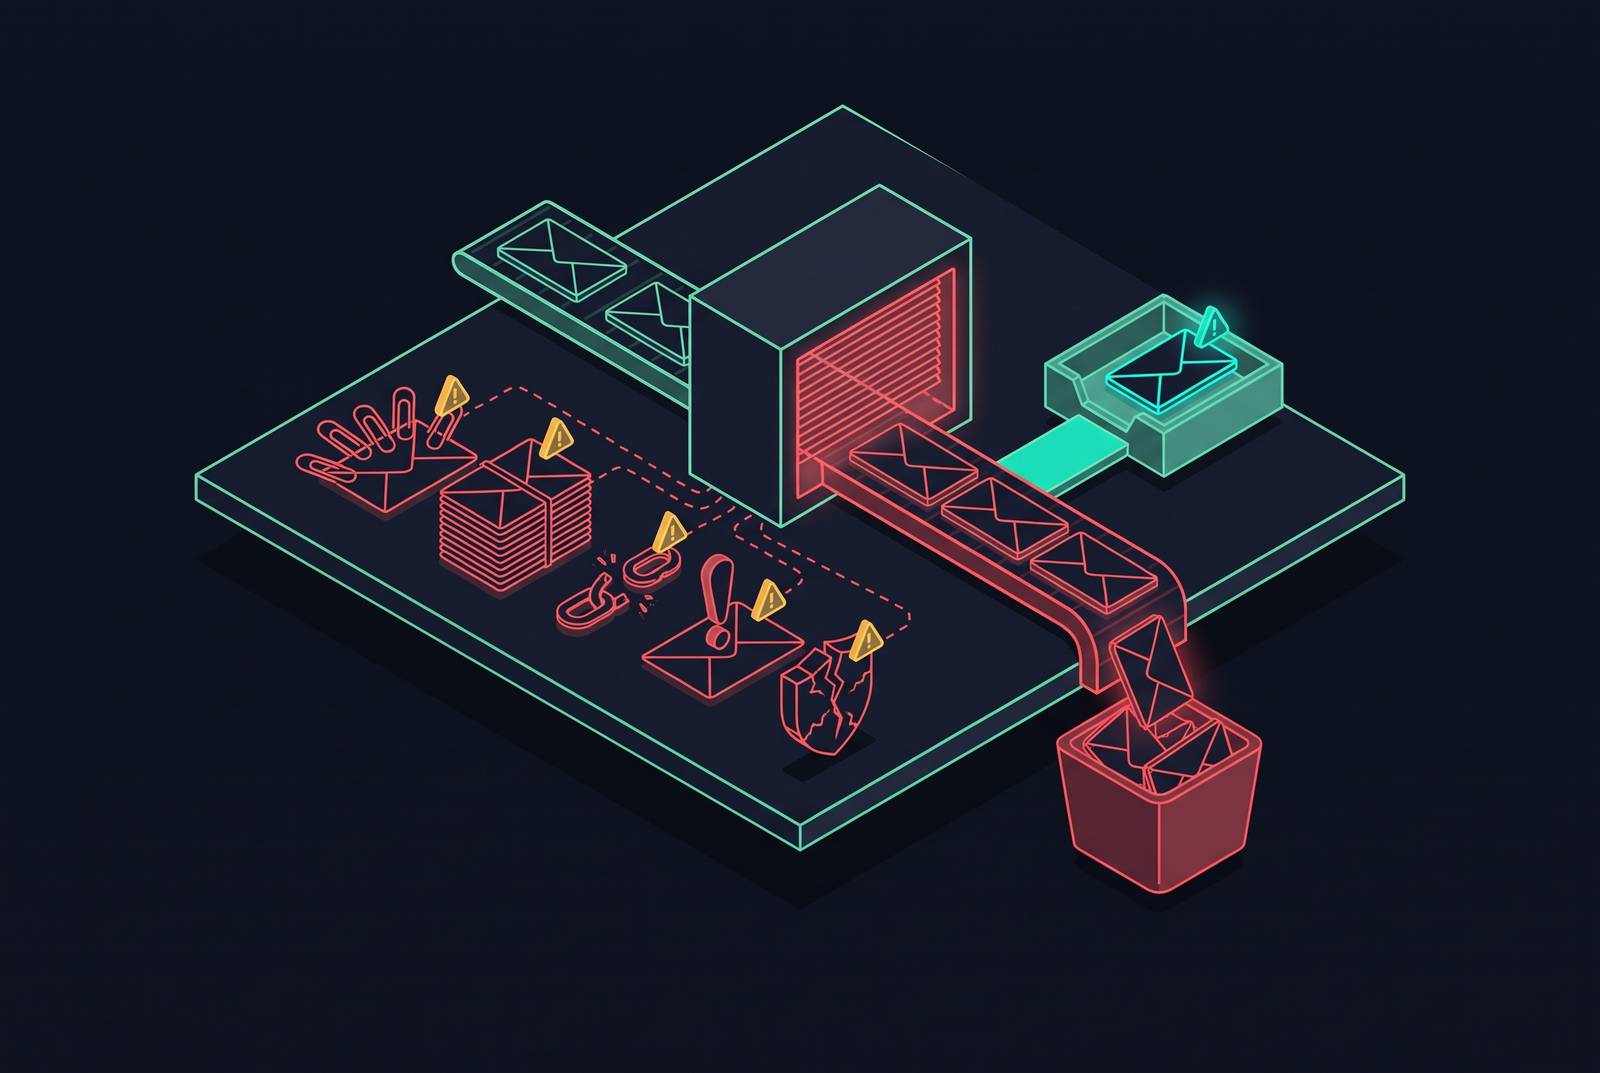
Cold email deliverability in 2026 depends on passing two distinct tests. Message acceptance depends on authentication infrastructure, while the placement of accepted mail depends on content and recipient behavior. The spam filter triggers that kill campaigns work across both layers, so removing suspicious words cannot fix a broken sending system.
Why cold email deliverability broke in 2025–2026 and what permanently changed
Google and Yahoo mandated SPF, DKIM, and DMARC for bulk senders starting February 2024. Gmail escalated enforcement in November 2025, moving from soft 4xx deferrals toward permanent 5.7.x rejections. Gmail delays or rejects non-compliant bulk email when more than 5,000 messages are sent per day. Rejected mail stops at the SMTP level. It does not wait in a junk folder for a prospect to discover it.
That shift makes the old assumption that poor authentication merely lowers placement dangerous. Authentication failures can now generate permanent bounces that damage domain reputation before recipients see anything. Better copy cannot reverse that outcome. At this first gate, the distinction is binary, with mail either accepted for further evaluation or permanently rejected.
The two-layer structure spam filters use to evaluate every cold email
The infrastructure layer covers authentication records, domain setup, sending volume, and list quality. Receiving systems use these signals to decide whether to accept the message. The content layer then evaluates wording, formatting, and the behavioral signals recipients generate, shaping inbox versus spam placement. The order determines where troubleshooting should begin. A rejected message never gets to the placement decision that a change in copy is meant to improve.
These layers are sequential, but their effects compound. Most campaigns that struggle have problems with both infrastructure and content at the same time. Modern filters weight engagement history, sender reputation, and content pattern matching in that order of importance. Content is the smallest of those signal groups. Its influence also extends beyond pattern recognition because what recipients do with a message feeds back into sender reputation.
Infrastructure triggers: the authentication, domain, and volume failures that cause hard rejections
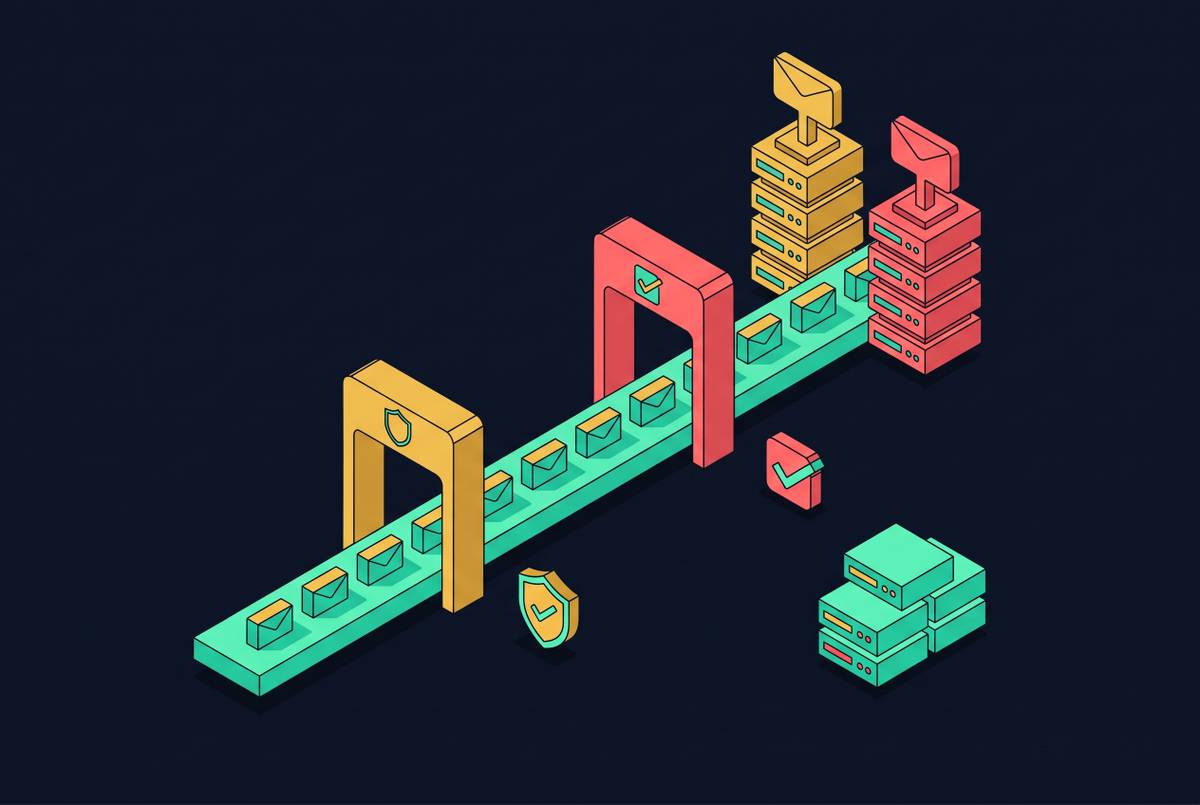
Authentication misconfiguration is the highest-stakes failure because it can stop delivery before content evaluation. SPF authorizes sending servers through a DNS TXT record, so every sending service must be included. If an email provider, cold email platform, or transactional tool is left out, mail sent through it has an SPF failure. DKIM supplies a cryptographic signature verified against a public key in DNS. Valid SPF does not compensate for missing DKIM under Google’s bulk-sender requirements.
DMARC connects the authentication results to the receiving server’s handling policy. All three controls belong in the sending setup. The minimum accepted policy, p=none, does not offer the stronger protection of p=quarantine or p=reject, and domains that remain at that minimum are increasingly treated as higher risk. DKIM keys should use 2048-bit keys. If a key is compromised, others can use it to send authenticated mail on the domain’s behalf.
Domain choice creates another failure boundary. Cold outreach should use secondary domains, such as getacme.com or acmemail.com, that redirect to the primary business domain. This separates outreach risk from transactional mail and team communication if an outreach domain is blacklisted. Secondary domains still need complete authentication. Random-looking names raise suspicion when prospects investigate, while a redirect to the primary domain provides a legitimacy signal.
Correct authentication does not make excessive volume safe. Mailbox rotation distributes sending across multiple domains and addresses, with a minimum of three to five mailboxes per SDR. New domains and inboxes need gradual warming. Replies from real inboxes are the key warming measure because services that only exchange mail with each other do not build genuine sender reputation.
Unsubscribe handling is also part of the infrastructure. Senders reaching Gmail or Yahoo at volume need RFC 8058 List-Unsubscribe and List-Unsubscribe-Post headers, an HTTPS endpoint, and a process that honors requests within two days. Re-emailing opt-outs generates complaints as well as compliance risk. List controls must therefore suppress unsubscribes and previous complaints before sequencing. Contact verification with tools such as NeverBounce or ZeroBounce helps eliminate invalid, catch-all, and role-based addresses, reducing the bounces that degrade reputation.
Content triggers: the formatting, language, and structural patterns that train filters to classify email as spam
Content evaluation primarily recognizes patterns rather than scanning for forbidden vocabulary, so stacking signals is more damaging than an isolated word choice. Heavy HTML, promotional language, and suspicious links reinforce one another. Cold outreach should use plain text or very little HTML. Images, colored buttons, and branded headers look like promotional mass mail, while image-only messages and hidden text are flagged no matter what the wording says.
Links add another set of signals. More than one link in a first cold email raises spam scoring, and link shorteners such as bit.ly are strongly associated with phishing and should be avoided. Shared tracking pixels introduce reputational exposure to other senders using the same platform. Attachments should not appear in a first cold email. They make messages larger, trigger security scans, and are a known way to spread malware, which adds to the risk from any promotional formatting already in the message.
Subject lines can create problems on their own. ALL CAPS remains a reliable trigger, although a single acronym such as SaaS or CEO is not equivalent to an entire capitalized subject. Fake reply or forwarding prefixes imply a conversation that never happened. Filters flag that pattern, and recipients who recognize it generate spam reports. Subjects impersonating internal invoice or meeting threads have become stricter enforcement targets as complaints increase.
Punctuation reinforces these structural cues. More than one or two exclamation marks per email, any exclamation mark in the subject, stacked question marks, dollar sign chains, and long strings of dots raise spam scoring. Their individual contribution may be small. Combined with manufactured urgency, financial claims, or promotional promises, however, they make a short message resemble spam or phishing. A single time reference differs from three urgency phrases competing for attention.
Language risk follows the same stacking principle. Clusters of “amazing,” “revolutionary,” “guaranteed,” and “no obligation” make outreach resemble newsletter marketing, while greetings such as “Dear valued customer” are recognizable mass-mail patterns. Raw financial language can usually be reframed around value in B2B outreach. Gmail’s transformer-based filters recognize generic sales templates even when names and company attributes have been filled in.
Open tracking adds risk without dependable measurement. Apple Mail Privacy Protection inflates open rates, making them unreliable as an engagement signal. Many practitioners in 2026 therefore disable open tracking and rely on replies. That choice also avoids treating a distorted metric as evidence that recipients welcome a campaign.
Why trigger-word lists alone are the wrong diagnostic tool
A single-word blacklist is the wrong model for modern filtering. Gmail, Outlook, and Yahoo evaluate dozens of weighted signals simultaneously, allowing an otherwise credible message to use ordinary commercial words such as “free” or “guarantee” without automatically reaching spam. The belief that one word ruins delivery reflects older point-based filtering more than current transformer-based systems. Context changes the interpretation. One use of “free” in a paragraph is not equivalent to “FREE MONEY NOW” in a subject line.
A warmed domain, a verified list, sound authentication, and behavioral credibility do more to help than removing every commercial term. This does not excuse misleading formatting. ALL CAPS subjects, fake conversation prefixes, heavy HTML, shorteners, and attachments remain genuine signals.
Behavioral signals: how recipient engagement trains filters to favor or penalize a sender's domain
Recipient behavior is the strongest ongoing signal used to classify a sender’s domain. Replies provide the strongest positive feedback, while manually moving messages out of spam or marking them important also favors placement. Deleting messages without opening them accumulates negative feedback. Consistent non-opens across a large send suggest poor targeting or an audience with no relationship to the sender. These effects compound across a campaign.
A generic message can prompt deletion or a spam report, which then influences the treatment of later mail from the domain. Personalization is therefore a deliverability decision as well as a conversion decision. Tight ICP targeting reduces the likelihood of reaching irrelevant contacts. Signal-based outreach that refers to specific buying triggers gets stronger replies than personalization based only on company size or industry.
Sending more mail to non-responders works against that benefit. Removing them after a defined cadence protects reputation. List segmentation and message quality work together in the same way, since copy needs to fit the audience that gets it. Neither can substitute for the other. Domain reputation is a living asset shaped by every campaign.
Diagnosing which layer is breaking a campaign and where to look first
The practical workflow begins by separating rejection from placement. For bounces and hard rejections, check SPF, DKIM, and DMARC with MXToolbox or DMARC Analyzer, then send a test to a fresh Gmail account and inspect the authentication headers for passes. Google Postmaster Tools provides a further compliance check. A “Needs Work” status in its v2 interface indicates a failure involving authentication, complaint rate, unsubscribe compliance, DNS, formatting, or encryption that requires immediate attention.
Next, review bounce rates by campaign rather than treating the sending account as one undifferentiated total. A rising rate points toward deteriorating list quality or domain reputation. Complaint data narrows the investigation further. If the rate exceeds the 0.10% practical limit, identify and suppress the segments or sequences producing complaints before continuing.
Once acceptance is established, test inbox placement across Gmail, Outlook, and Yahoo with GlockApps. Mail-Tester and Litmus support pre-send checks for spam scores, authentication, and rendering, but do not provide per-provider seed-list placement results. The distinction is operationally important. A clean pre-send score does not show where a provider placed the message.
For messages that reach spam, strip formatting to plain text as a baseline and examine link count and attachments. Then audit template structure and clusters of urgency, financial, and hype language. Review recipient behavior after those static checks. High deletion rates and zero-reply sequences on a warmed domain indicate content and targeting problems.
A domain damaged by sustained high complaint rates requires a rebuild. Pause all sending, audit and re-authenticate, re-warm the domain, and restart at micro-volume. Each step addresses a different part of the damage. Skipping a stage risks restarting it.
Building a sending infrastructure that stays compliant as enforcement continues to tighten
SPF records should be audited whenever a sending service is added, and DKIM keys should rotate at least annually. DMARC should progress from p=quarantine to p=reject once SPF and DKIM are clean. Configuration is not a completed project. Each new tool or policy change creates another point at which the system can stop meeting provider requirements.
Growth should follow the same operating discipline. Sending capacity should expand through mailbox rotation and authenticated secondary domains. Real-inbox engagement must support that expansion. Otherwise, more capacity simply distributes a campaign whose targeting or reputation remains weak. Signal-based personalization belongs in this system because replies help keep up the reputation that infrastructure alone cannot build.
Monitoring must also run during campaigns and afterward. Google Postmaster Tools’ binary compliance status now gives an early warning in place of the old four-tier reputation score. Complaint rates need continuous attention because the 0.10% practical limit can be crossed mid-campaign. Pre-campaign placement tests provide a separate safeguard before sending generates complaint data. Together, these practices connect authentication, placement, and behavior to ongoing decisions about volume and targeting.
Stricter enforcement creates an opportunity for disciplined senders. Teams that invested in deliverability infrastructure, signal-based personalization, and compliance workflows are seeing the highest response rates as unadapted competitors drop out of the inbox. Maintaining both layers gives compliant senders access to a less-crowded inbox.