Google and Yahoo Bulk Sender Requirements for Cold Email
Hard bounces now reject cold email before it reaches any inbox folder.
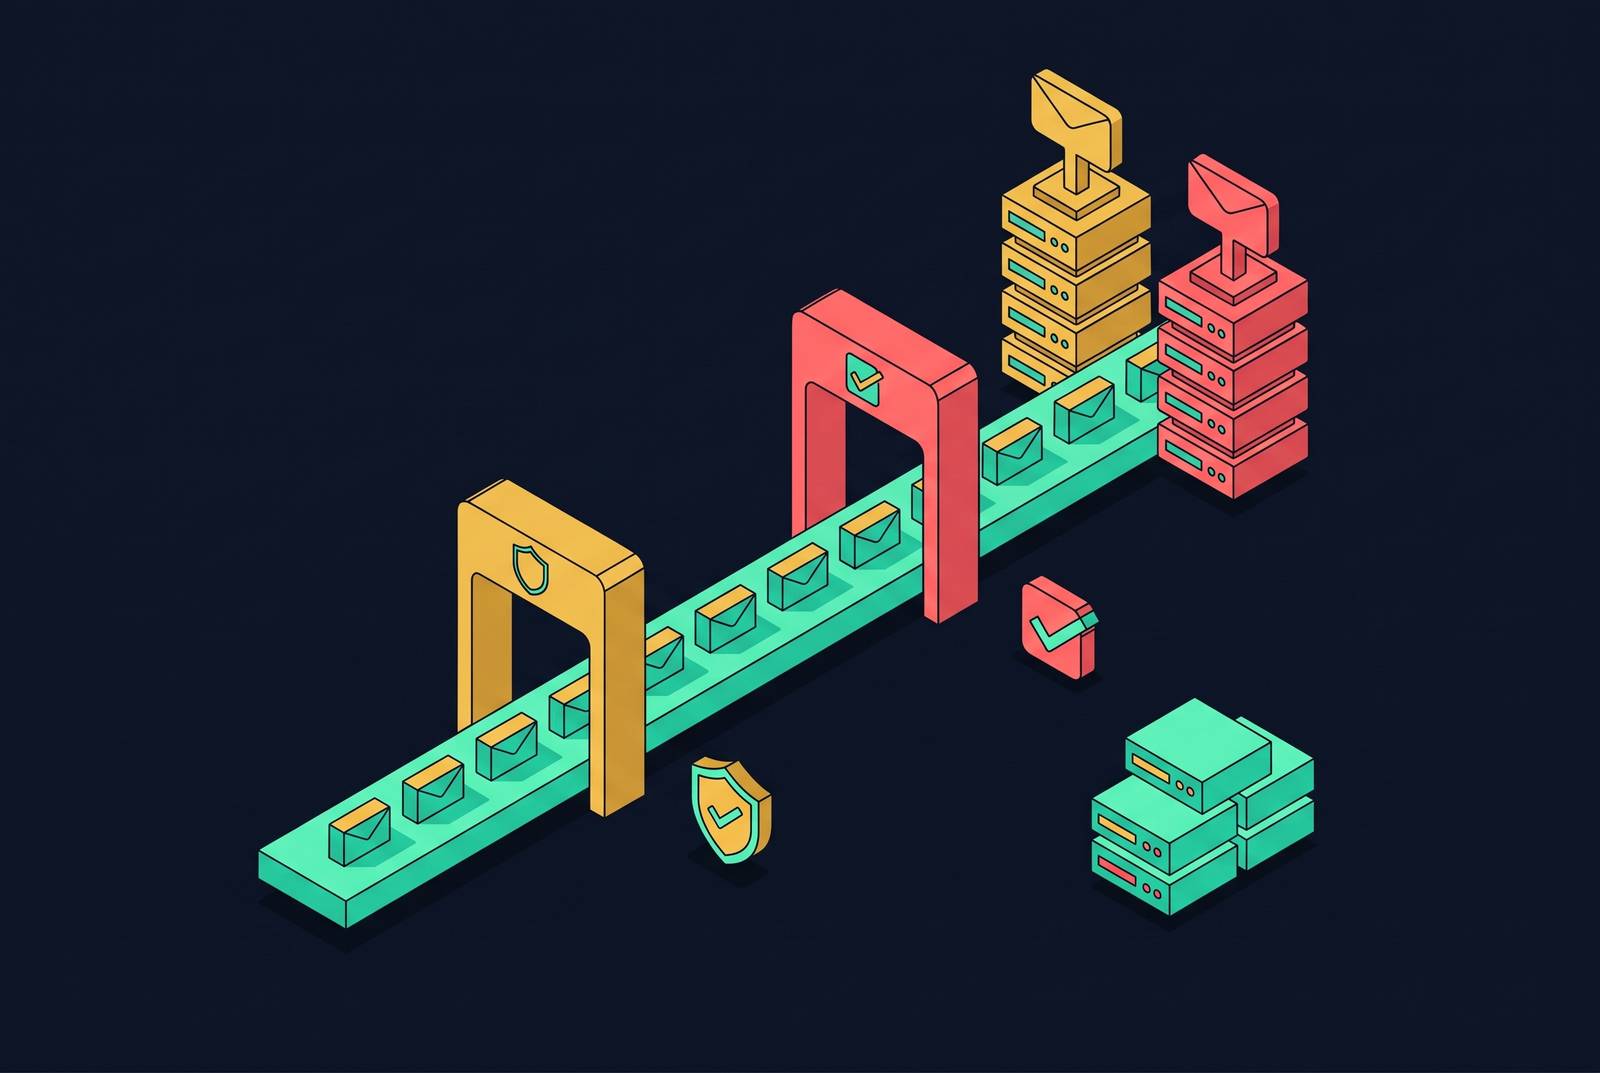
Google and Yahoo’s bulk sender requirements mean senders must have authentication and list hygiene for their mail to be delivered. Cold email senders need to understand the details to meet the rules, including permanent bulk-sender classification, domain alignment and technical unsubscribe requirements. A legally permissible, well-written message can still be rejected before it reaches any folder.
Why Google and Yahoo's 2024 rules changed the stakes for cold email
By November 2025, Google’s enforcement had moved beyond temporary deferrals to include hard bounces, or permanent rejections. A deferred message is held up for a time, but with an SMTP-level rejection, the receiving server refuses the message outright. It never reaches the inbox or spam folder, so improving the copy cannot resolve that failure.
Google and Yahoo began converting authentication best practices into mandatory requirements in February 2024, with hard rejections phased in from April 2024. The consequences tightened as enforcement developed. Both providers stated that their purpose was to protect users from spam, phishing and insecure inboxes. Their acceptance rules follow that protective logic, rather than the sender’s commercial interest in reaching a prospect.
Who the rules classify as a bulk sender, and why cold emailers should not assume they are exempt
Google defines bulk sending by daily message volume to personal Gmail accounts, aggregated across a primary domain and its sending subdomains. Once a domain crosses the threshold, its classification is permanent even if volume later falls. Splitting traffic among subdomains does not change that aggregation. Yahoo uses a less explicit boundary. Yahoo’s sender guidance refers to “a significant volume of mail” without publishing a specific volume number.
That leaves two separate questions, namely whether a sender qualifies as bulk and whether its mail faces delivery risk. Sending only a few hundred emails a day may avoid Gmail’s bulk classification, but it does not provide immunity from authentication failures. The bulk threshold is not a safety line. Cold outreach also reaches people who did not opt in, making complaints a more immediate risk than they are for permission-based newsletters. Low mailbox volume therefore cannot substitute for technical compliance or a well-qualified recipient list.
The authentication stack every sender must have, including SPF, DKIM, and DMARC alignment
SPF, DKIM and DMARC establish related, but distinct, parts of a domain’s identity. SPF is a DNS TXT record identifying the servers and IP addresses authorized to send for a domain. DKIM adds a cryptographic signature that lets the receiving server check whether a message changed on its way there. DMARC publishes the domain’s policy for mail that fails authentication. For bulk senders, Google and Yahoo accept p=none as the minimum DMARC policy, but that setting turns on reporting without asking for enforcement.
The connection between these records is alignment. In plain language, the domain recipients see in the From header must match the domain authenticated through SPF or the domain signing through DKIM. A published DMARC record cannot compensate for a mismatch. The records must work together, rather than merely exist. This is why checking DNS records alone does not establish that a live campaign passes authentication.
Gmail’s bounce codes distinguish several authentication failures. The code 550-5.7.26 indicates that unauthenticated email was not accepted, while 550-5.7.27 identifies an SPF failure and 550-5.7.30 a DKIM failure. The code 550-5.7.40 points to a missing DMARC record or policy, and 421-4.7.32 identifies From-domain misalignment. These codes narrow the diagnosis considerably. Beyond the minimum policy, p=quarantine or p=reject does more to protect against forged-domain abuse, which cold email domains can face through spoofing.
Infrastructure requirements that determine whether your sending IP is trusted before a single word is read
Authentication establishes domain identity, while DNS, transport and message formatting establish the legitimacy of the sending machinery. Google requires valid forward and reverse DNS, with the PTR hostname resolving back to the sending IP. Yahoo also expects meaningful, non-generic reverse DNS. Google requires mail to be sent using TLS, but Yahoo’s best-practices page does not say outright that it requires this. Message formatting must meet RFC 5322 for Google and RFC 5321 / RFC 5322 for Yahoo, including one From address, a valid Message-ID and no duplicated single-instance headers.
For shared infrastructure, the email service provider typically manages PTR records and TLS, but the sender still needs to verify that provision. Dedicated IPs require explicit PTR configuration. Even when authentication works, a missing infrastructure control can still cause a failure. These failures can be silent until delivery is attempted, when a bounce code provides the first warning.
How the spam rate threshold works and why cold email makes it harder to stay below it
Technical compliance does not establish that recipients want the mail. Google’s spam-rate framework evaluates a different signal, namely how recipients respond to delivered messages. Cold outreach is especially exposed because an uninterested recipient has no prior subscription relationship to end. It may feel more natural to report spam than to unsubscribe.
A tightly targeted list reduces the mismatch between a message and its recipients, while irrelevant outreach invites complaints regardless of how carefully it is written. List quality therefore belongs within compliance operations. It is not simply a campaign-performance concern, because complaints can impair delivery even when authentication passes.
Google’s framework distinguishes a lower spam-rate target from an upper enforcement limit. Senders should stay below the lower threshold and never reach the upper one. After a spike, Google requires seven days in a row below the upper limit before it restores delivery mitigation. The domain remains subject to that classification while its complaint behavior determines its position under the spam-rate framework.
Yahoo does not publish a numeric threshold and can defer high-complaint domains. Its calculation also differs from Google’s. Yahoo counts only messages that reach the inbox in the denominator and leaves out those that go to the spam folder, while Google counts all delivered Gmail messages. The same complaint volume can therefore produce a higher rate at Yahoo. A healthy reading at one provider does not establish compliance at the other.
One-click unsubscribe and what RFC 8058 means for cold outreach
One-click unsubscribe is a technical requirement for commercial and promotional bulk mail. RFC 8058 implementation uses a List-Unsubscribe header together with a List-Unsubscribe-Post header whose value is List-Unsubscribe=One-Click. Transactional mail is exempt at both providers. Yahoo began enforcing its List-Unsubscribe policy in June 2024 and accepts either the RFC 8058 POST method or mailto, though it strongly recommends POST.
For cold outreach, volume and message type determine the practical exposure. A sender delivering 50–200 personalized prospecting emails per day does not trigger Gmail’s bulk requirement on that volume alone. Multi-mailbox operations can bring a domain’s aggregate traffic within bulk criteria even when individual mailboxes appear modest.
For senders approaching that boundary, implementing the headers is the lower-risk choice. Gmail’s native unsubscribe button gives recipients an alternative to reporting spam, so the mechanism protects sender reputation as well as recipient choice. Processing the request is equally important. Unsubscribe requests must be honored promptly, and failure to do so makes a sender ineligible for Google delivery mitigation.
Why CAN-SPAM compliance does not guarantee deliverability under these provider rules
CAN-SPAM permits unsolicited commercial email under US law subject to conditions including a physical address, an unsubscribe mechanism, accurate headers and non-deceptive subject lines. It does not require prior opt-in consent for B2B outreach. Google and Yahoo, however, decide whether their servers will accept that mail. Legal permission does not compel technical acceptance.
Consequently, a CAN-SPAM-compliant message can still face SMTP-level rejection for authentication failures or provider-policy breaches. A recipient’s spam report also remains a trust signal regardless of the message’s legal status. Neither regime replaces the other’s requirements or purpose. Legal compliance addresses whether the message may be sent, while deliverability compliance addresses whether the receiving provider will accept it.
How Google Postmaster Tools and Yahoo's Complaint Feedback Loop give cold senders the monitoring they need
Google Postmaster Tools is free and shows spam rate, authentication and Compliance Status once the domain is verified. Postmaster Tools v2 launched in 2024, and v1 retired on September 30, 2025. The move removed the Domain Reputation and IP Reputation dashboards, so spam rate is now the main sign of a domain’s health. That changes the focus of routine monitoring. A sender needs to examine recipient complaints and authentication results rather than depend on the former reputation dashboards.
The practical cadence is to check after every significant send. Postmaster Tools only displays data when a domain sends enough mail to Gmail on a given day. An empty dashboard is not a clean bill of health. Senders who send little mail can still face enforcement even when the dashboard gives them too little data to see where they stand.
Yahoo’s Complaint Feedback Loop provides the corresponding mechanism for tracking complaints at Yahoo. Senders need both tools because the providers use different denominators, so neither reading gives a score that applies to both. Enrollment is an operational prerequisite. Neither tool promises warning before enforcement, so monitoring supports compliance without guaranteeing an opportunity to correct every failure before delivery is affected.
Microsoft Outlook's bulk sender requirements and how they extend the same enforcement logic
Microsoft’s high-volume sender requirements took effect on May 5, 2025, for consumer domains including Outlook.com and Hotmail.com. They use the same per-day volume definition as Google and require SPF, DKIM and DMARC at a minimum policy of p=none, with alignment through SPF or DKIM. The technical foundation is therefore substantially shared. A sender meeting Google and Yahoo’s requirements has already addressed much of Microsoft’s authentication baseline.
Microsoft’s enforcement decision replaced its earlier junk-first plan with rejection of messages that fail the required authentication checks. The rejection code is 550 5.7.515. Unlike Google, Microsoft has not said that bulk classification stays in place for good after volume drops. That distinction does not weaken the broader conclusion, because authentication failures now threaten acceptance across all three providers. Compliance belongs in the sending infrastructure, rather than in a separate workaround for each inbox service.
A practical compliance checklist for cold email senders across all three providers
For implementation, the controls fall into three groups, namely authentication, infrastructure and ongoing sending operations. Begin with authentication by publishing a valid SPF record that covers the sending servers and configuring DKIM signing with a sufficiently strong key. Check DKIM on a live campaign header. Publish DMARC at p=none minimum and confirm that the visible From domain aligns through SPF or DKIM. Use the authentication error codes above to diagnose failures rather than treating the presence of DNS records as proof of success.
For infrastructure, check that every sending IP has valid PTR records and that the reverse record is non-generic, as Yahoo requires. Confirm that TLS transmission is active. On shared infrastructure, verify which controls the provider manages. Message formatting must include one From address, a valid Message-ID and no duplicated single-instance headers. These controls are generally configured once, but warrant verification before a major send.
For ongoing operations, enroll and verify the domain in Postmaster Tools, enroll in Yahoo’s feedback loop and monitor each provider independently after significant sends. Keep spam rate below Google’s lower threshold. For qualifying commercial mail, inspect the raw message source for both unsubscribe headers, retain the body link and confirm that suppression reaches every synced tool. Treat list qualification as part of the same review because recipient complaints remain a risk for authenticated mail, and use this checklist as a starting state by checking official Google and Yahoo sender guidelines before a major send as policies, enforcement thresholds and authentication standards evolve.